A release review is strongest when it names the exact artifact being considered and the evidence that supports the decision. A green test run for one revision does not establish that a different package is safe to release. This guide turns a small release checklist into a local Python exercise. Its sample records are fictional; the helper never deploys software.
Connect evidence to the artifact
Record a source revision and calculate a SHA-256 checksum for the artifact that would be released. Compare the expected checksum with the bytes you actually received. This catches a changed or mismatched file; it does not prove who built the file or that the source itself is safe. For stronger provenance, use a trusted build process and signed attestations appropriate to your organization.
from hashlib import sha256

artifact = open('release.zip', 'rb').read()
actual = sha256(artifact).hexdigest()
if actual != review['sha256']:
    raise SystemExit('Block release: artifact checksum mismatch')
The review helper below expands this check into a small list of explicit release blockers. It reports blockers when the revision or checksum is missing, required checks did not pass, or named release responsibilities are blank. It also asks for a data recovery review when a release changes data. The exact fields are visible in release-example.json.
Separate checks from the decision
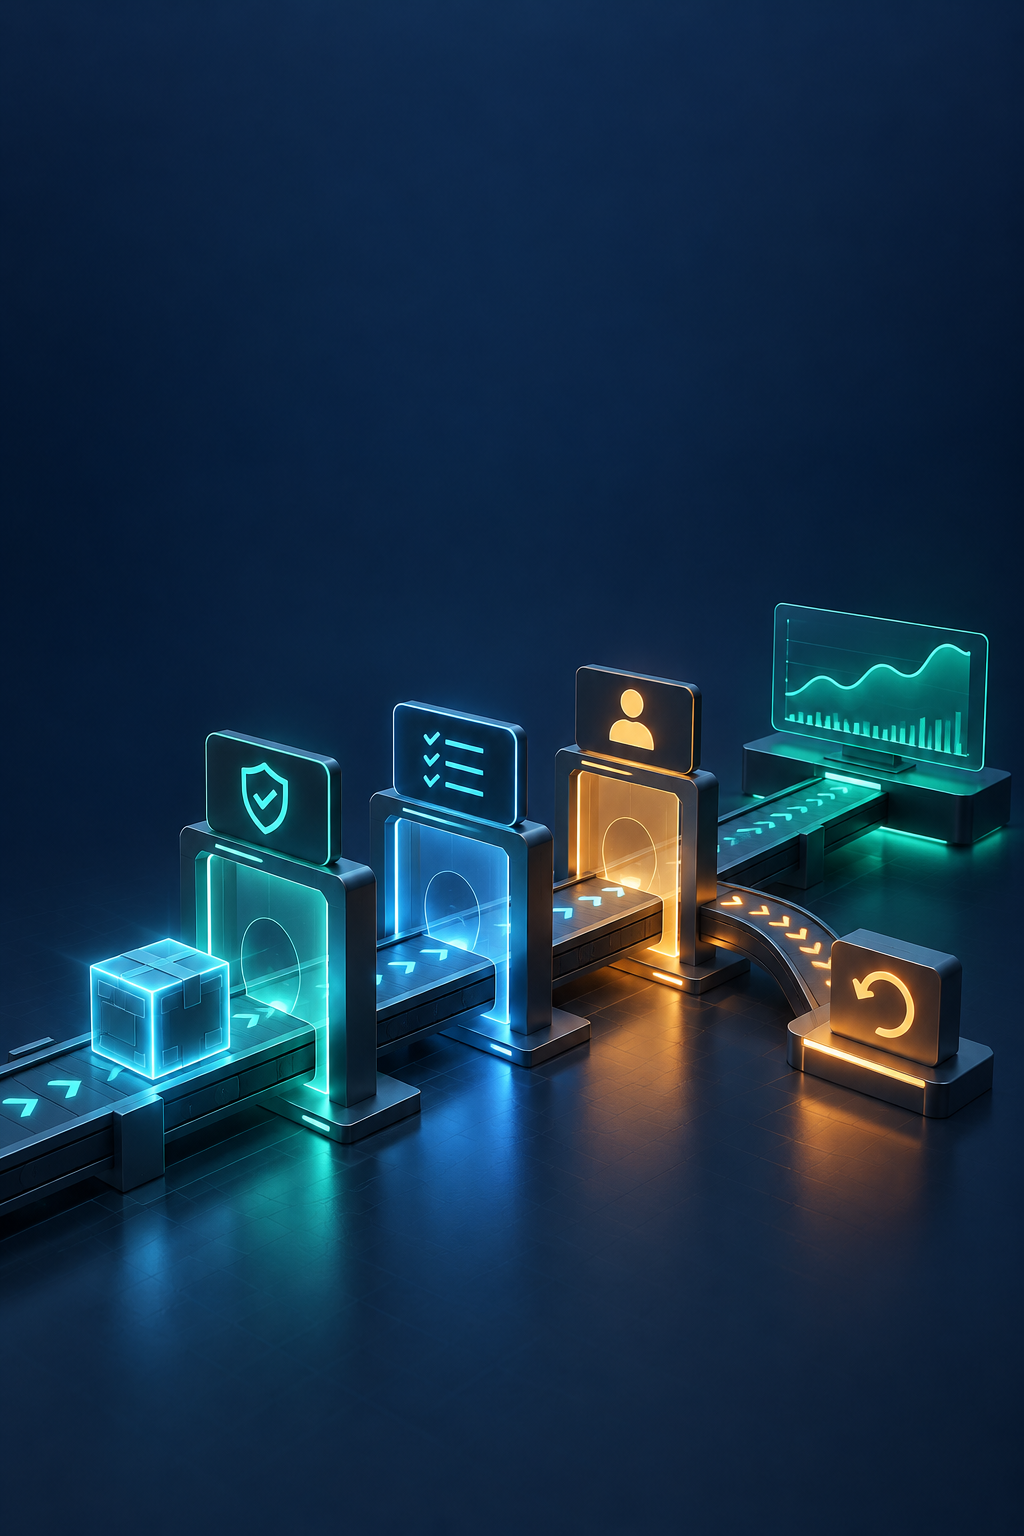
A practical review should identify which checks ran and which artifact they examined. For this example, unit, integration and smoke checks must each say “passed”. A release owner then reviews the evidence and records the decision. The helper only identifies missing evidence: it does not decide whether a test suite is adequate, approve a release, create a backup or roll back a deployment.
python3 examples/release_review.pySave the two Python code blocks below as release_review.py and release_check.py in the same folder. Create a JSON review record in the shape shown and run python3 release_check.py review.json release.zip. The command checks the exact file you name and never deploys it. The review helper reports missing or failed evidence; a person must still decide whether the checks and recovery plan are adequate.
Write down recovery and observation
Before a release, make the recovery plan concrete enough for someone else to follow. Name who can execute it, the condition that triggers it, and how the team will observe the result. If the change alters stored data, application rollback alone may not restore that data; document a separately reviewed recovery path. Keep the change window, expected signals and escalation route visible to the people on duty.
Where GitHub Actions is used, its deployment environments can gate jobs with required approvals, branch restrictions and scoped secrets. That provides a place to enforce parts of a release policy, while the team still needs to choose meaningful checks and maintain recovery steps. See the GitHub Actions deployment environments documentation.
A compact review checklist
- Does the source revision identify the change under review?
- Does the checksum match the exact artifact that will be used?
- Did each required check run against the intended revision and artifact?
- Who approves, observes and owns recovery?
- What signal triggers recovery, and what steps restore service?
- If data changes, has recovery of that data been reviewed?
The local review helper
Save this first block as release_review.py:
"""Local review exercise: checks evidence, never deploys anything."""
import hashlib


def release_blockers(review, artifact):
    blockers = []
    if not review.get('revision'):
        blockers.append('Missing source revision')
    actual_hash = hashlib.sha256(artifact).hexdigest()
    if review.get('sha256') != actual_hash:
        blockers.append('Artifact checksum mismatch')
    for check in ('unit', 'integration', 'smoke'):
        if review.get('checks', {}).get(check) != 'passed':
            blockers.append(f'{check} check is not passed')
    for field in ('approver', 'rollback_owner', 'rollback_steps',
                  'observation_owner', 'rollback_trigger'):
        if not isinstance(review.get(field), str) or not review[field].strip():
            blockers.append(f'Missing {field}')
    if review.get('data_change') is True and review.get('data_recovery_reviewed') is not True:
        blockers.append('Data recovery has not been reviewed')
    return blockers
Command-line check
Save this second block beside it as release_check.py:
#!/usr/bin/env python3
"""Check release evidence against the exact artifact bytes; never deploys."""
import argparse
import json
from pathlib import Path
from release_review import release_blockers


def main():
    parser = argparse.ArgumentParser(description=__doc__)
    parser.add_argument('review_json', type=Path, help='Review record in the documented JSON shape')
    parser.add_argument('artifact', type=Path, help='Exact artifact to check')
    args = parser.parse_args()
    review = json.loads(args.review_json.read_text())
    blockers = release_blockers(review, args.artifact.read_bytes())
    if blockers:
        print('BLOCKED')
        for blocker in blockers:
            print(f'- {blocker}')
        return 1
    print('Evidence is complete for review. A human release decision is still required.')
    return 0


if __name__ == '__main__':
    raise SystemExit(main())
Example review record
This fictional record shows the expected JSON fields. Replace its revision and checksum with values for your own review:
{
  "revision": "example-commit-123",
  "sha256": "e3fbcc12d3fe8cf2b44ea7187f90419d97e0b9d852f2db55a8586266c1287fad",
  "checks": {
    "unit": "passed",
    "integration": "passed",
    "smoke": "passed"
  },
  "approver": "Release owner",
  "rollback_owner": "On-call engineer",
  "rollback_steps": "Return to the previously verified artifact; assess data separately.",
  "observation_owner": "Release observer",
  "rollback_trigger": "Agreed health check fails after the deployment window.",
  "data_change": false
}
The fictional helper is intentionally small. A real release process should also consider access controls, dependency and security review, backups, staged rollout, monitoring and the risks of the particular change. For background on automated delivery and release practices, see the CI/CD pipelines course recommendation.